A software update can close a serious vulnerability and create an outage in the same maintenance window. That tension is why patching should be treated as controlled production change, not simply a file-transfer task.
NIST describes enterprise patch management as identifying, prioritizing, acquiring, installing, and verifying patches, updates, and upgrades. It also frames patching as preventive maintenance capable of reducing compromises, breaches, and operational disruptions.
Knowing how to securely deploy software updates to remote servers therefore means protecting the entire path from trusted build artifact to verified production service.
Start With Risk, Not With the Install Button
Not every update deserves the same deployment schedule.
A routine library update on an internal reporting server may wait for the normal maintenance cycle. A vulnerability being actively exploited deserves different treatment.
CISA maintains its Known Exploited Vulnerabilities Catalog specifically to identify vulnerabilities with evidence of exploitation in the wild. Although mandatory remediation deadlines associated with the catalog apply to covered federal agencies, CISA recommends that other organizations use the catalog when prioritizing vulnerability remediation.
Before deployment, classify the change according to:
- security urgency;
- internet exposure;
- server criticality;
- customer impact;
- dependencies;
- restart requirements;
- rollback complexity.
This keeps teams from making two common mistakes: rushing every update into production or delaying a genuinely urgent security fix because the next scheduled maintenance window is days away.
Secure the Route Into Every Remote Server
A deployment system is effectively an administrative system. If an attacker compromises it, that access may provide a legitimate-looking route into many servers simultaneously.
Use Encrypted, Authenticated Connections
Remote administration traffic should travel through an encrypted protocol such as SSH or appropriately configured TLS.
The Internet Engineering Task Force’s SSH specification explains that SSH provides encryption, server authentication, and integrity protection for communication over an insecure network.
For automated deployments, prefer managed SSH keys, certificates, workload identities, or other centrally controlled credentials over shared administrator passwords.
Remote access should also be tightly restricted. CISA warns that legitimate remote-access software is increasingly abused by threat actors and recommends controls that reduce unauthorized use.
Give the Deployment Pipeline Only the Access It Needs
Avoid giving a deployment service unrestricted root access merely because it is convenient.
OWASP recommends least-privilege access for CI/CD identities and warns that pipeline credentials can provide substantial access to sensitive environments. It also recommends limiting credential sharing and avoiding unnecessary privileged execution.
A stronger model gives the pipeline permission to perform specific deployment actions on specific systems.
Store secrets in a dedicated secrets-management system rather than source code, scripts, configuration repositories, or command-line arguments that may appear in logs. Temporary credentials are preferable when the infrastructure supports them.
Verify the Software Before Running It
Encryption protects an update while it travels. It does not prove that the package itself is legitimate.
That distinction matters.
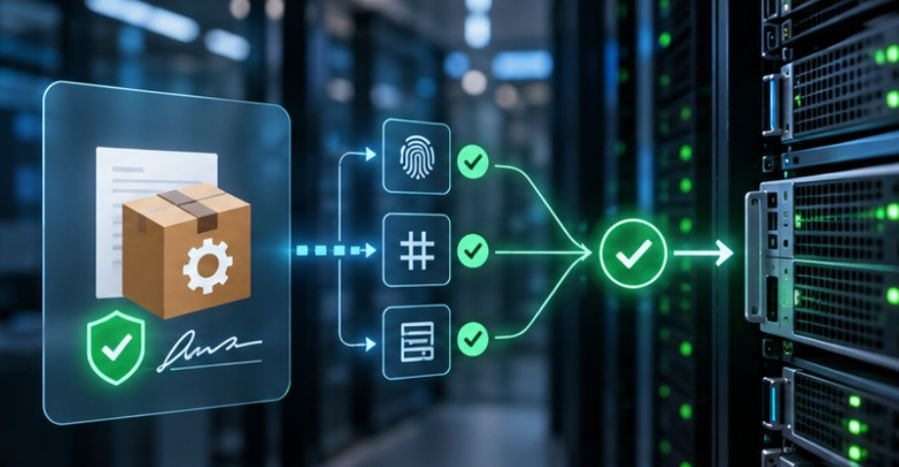
NIST’s code-signing guidance explains that digital signatures can establish both software integrity and the identity of the signer. This helps systems detect modified or forged software before execution.
A secure workflow should therefore:
- Obtain the package from an approved source.
- Validate its digital signature where available.
- Calculate and compare the expected cryptographic hash.
- Reject unexpected or unsigned artifacts.
- Record the verified version and hash in deployment logs.
Beyond verifying the integrity and source of an update, compatibility should also be confirmed before installation. Learning how to tell if software will run on your computer can help identify hardware, operating system, and system-requirement constraints before introducing new software into an environment.
Do not manually download an executable onto one administrator’s laptop and distribute the same unchecked file to dozens of servers. Maintain a controlled artifact repository so production receives exactly what testing approved.
Understanding the collaborative model behind software development can also clarify how trusted code is reviewed, modified, and distributed.
This resource on how open source software works for beginners explains the role of repositories, licensing, contributors, pull requests, and maintainers in the open source development process.
Use Deployment Rings Instead of Updating Everything at Once
One of the safest ways to deploy a faulty update is to avoid deploying it everywhere simultaneously.
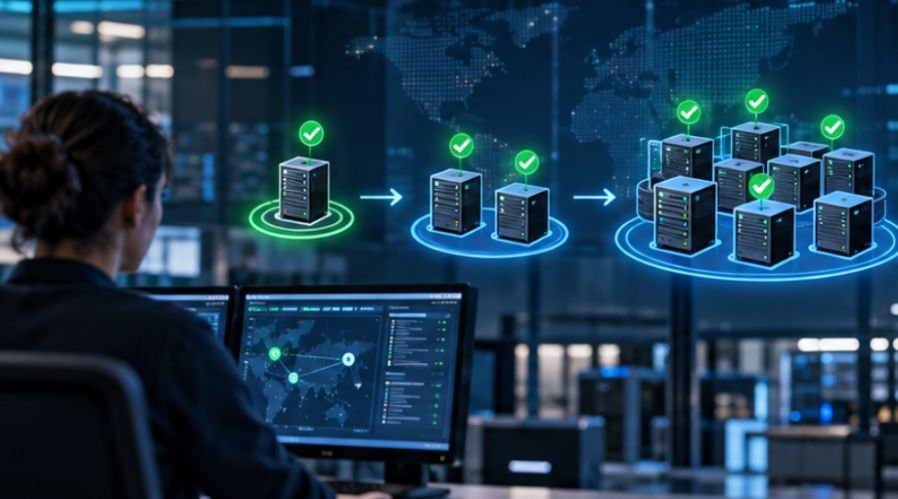
A staged rollout creates progressively larger groups of servers.
| Deployment stage | Purpose | Proceed when |
| Test environment | Validate installation and compatibility | Automated tests pass |
| Canary server | Expose one low-risk instance | Health metrics remain normal |
| Pilot group | Detect workload-specific failures | No meaningful regression appears |
| Production groups | Expand deployment gradually | Each previous group stays healthy |
| Final verification | Confirm complete rollout | Versions, services, logs, and monitoring pass |
This approach limits the blast radius of a bad release.
Define Health Checks Before Deployment
Do not decide whether a deployment succeeded merely because the installer returned exit code zero.
Check what users and dependent systems actually need.
For a web application, that could include HTTP response status, latency, authentication, database connectivity, queue processing, CPU consumption, memory use, and application error rates.
For an infrastructure service, validation might include active ports, daemon status, cluster membership, replication, storage health, and dependency checks.
Automation should stop the rollout when predetermined thresholds fail rather than blindly continuing through the remaining servers.
Build Rollback Before You Need It
Rollback instructions written during an outage are rarely as reliable as rollback instructions tested beforehand.
Before a risky deployment, identify exactly how the previous working state will be restored. Depending on the environment, this could mean:
- redeploying the previous signed artifact;
- reverting an immutable machine image;
- restoring a virtual-machine snapshot;
- switching traffic to the previous application version;
- running a tested database rollback procedure.
Backups matter, but a backup is not automatically a fast rollback mechanism. A large database restoration could take hours.
For critical systems, test recovery speed instead of simply confirming that a backup exists.
Database migrations require particular caution. Schema changes should ideally remain backward compatible long enough for old and new application versions to coexist. Otherwise, rolling the application back may leave it incompatible with the updated database.
Maintenance Windows Are Useful, but Security Risk Comes First
Maintenance windows reduce business disruption, particularly for servers that require restarts or temporarily lose capacity during installation. They should not become excuses for delaying urgent vulnerabilities.
A better model uses normal maintenance windows for routine updates and a documented emergency process for high-risk vulnerabilities. If an emergency patch cannot safely be installed immediately, temporary controls may include network isolation, disabling the vulnerable service, tightening firewall rules, or increasing monitoring until remediation is possible. CISA recommends these kinds of mitigations when immediate patching is impractical.
Common Mistakes That Make Remote Deployment Less Secure
The biggest risks are often operational rather than exotic. Avoid shared administrative credentials, unrestricted root accounts, manually copied packages, secrets embedded in deployment scripts, unverified downloads, fleet-wide simultaneous updates, undocumented exceptions, and deployments with no tested recovery path.
Keeping software current is another important part of maintaining a secure deployment environment. Learning how to check if computer software is outdated can help identify systems running older versions that may require security patches, compatibility updates, or other maintenance before deployment.
Automation does not remove these risks automatically. It can amplify them. A bad manual command may affect one server; a badly designed automated pipeline can repeat the same mistake across hundreds. That is why automated deployment needs stronger controls, not fewer.
Frequently Asked Questions
1. What is the safest way to update multiple remote servers?
Use authenticated encrypted connections, verified packages, least-privilege deployment credentials, canary servers, automated health checks, staged rollout groups, and a tested rollback procedure.
2. Should software updates always be installed immediately?
No. Prioritize according to exploit activity, exposure, severity, server importance, and operational risk. Actively exploited vulnerabilities may justify an emergency deployment rather than waiting for routine maintenance.
3. Are SSH keys safer than passwords for deployments?
Properly managed cryptographic credentials generally work better for automation because they can be centrally controlled and restricted. Protect private keys carefully, rotate them, and avoid sharing credentials between unrelated systems.
4. What should deployment logs contain?
Record the software version, artifact hash, affected servers, deployment identity, timestamps, success or failure status, health-check results, exceptions, and any rollback actions.
Make Every Deployment Prove It Is Safe
Secure patching is not simply the act of connecting to a server and installing a newer package. The safer model creates evidence at every stage: the artifact is authentic, the connection is protected, access is limited, recovery is possible, the first machines remain healthy, and the final fleet runs the expected version.
That is the practical answer to how to securely deploy software updates to remote servers. Treat every release as a controlled security event. Verify before execution, expand slowly, measure real service health, and make rollback a tested capability rather than an emergency hope.
Leave a Reply